What is this website?
SPDX is an open standard for communicating software bill of material information, including provenance, license, security, and other related information. SPDX reduces redundant work by providing common formats for organizations and communities to share important data, thereby streamlining and improving compliance, security, and dependability. The SPDX specification is recognized as the international open standard for security, license compliance, and other software supply chain artifacts as ISO/IEC
No listed local patterns observedHomepage-only analysis is not a malware clearance. Read the scope and findings below.
How to read this report
Safety Score evaluates observed signals. Evidence Confidence measures how complete, direct, fresh, and consistent those signals are.
No automated scan can guarantee that a website is safe.
Current report context
What changed since the last scan
- No earlier report to compare
What this scan could verify · 6 observed, 0 unavailable
Unavailable and unperformed checks are not clean results. The detailed evidence below remains the source for each conclusion.
Independent evidence brief
What we observed about spdx.org
The latest scan examined 0 public pages on spdx.org. Website descriptions below come from the site itself. Registration, connection and threat findings were checked separately.
Purpose and visible content
On its About page, the site says: SPDX is an open standard for communicating software bill of material information, including provenance, license, security, and other related information. SPDX reduces redundant work…
Observed page title: SPDX – Linux Foundation Projects Site.
Registrar and domain history
Registered on Apr 16, 2010. Registrar: 1API GmbH.
Recorded expiry date: Apr 16, 2027. Registry data can change.
Connection and hosting evidence
The checked homepage returned HTTP 200.
A valid TLS certificate was observed, expiring Feb 27, 2027.
Threat checks and score context
External malware-provider coverage was unavailable. The report does not treat this missing check as a clean result.
Safety Score: 73/100. Evidence Confidence: 75%. These measure different things.
Community reviews of spdx.org
No approved reviews yet
Visitor experiences are separate from the independent technical Safety Score.
Visitor opinions remain separate from the technical Safety Score.
Public page evidence
Topics and keywords observed on spdx.org
These phrases were extracted locally from sampled public page metadata. They are observations, not search-volume or ranking estimates.
At a glance
Key findings
Report is current
The displayed evidence comes from the published immutable scan.
Confidence is separate
Unavailable evidence is shown as missing and never counted as clean.
Verify before sensitive actions
Check the exact URL and context before payments, credentials, or downloads.
Fully explainable
Why this score?
Threat providers were unavailable. The neutral uncertainty baseline is not a clean verdict.
Domain registration age and expiry were checked.
Observed DNS records and network address were checked.
Observed certificate validity and TLS protocol were checked.
Observed security header values were checked for basic protective settings. Empty values, disabled HSTS and unrecognized values receive no credit. This is not a complete browser-policy validation.
Observed site metadata and About page were checked. Publisher-supplied details are not independently verified.
Popularity is weak context, not proof of safety. Unranked sites use a neutral baseline.
Observed HTTP status and final connection scheme were checked.
Server-side analysis
Automated security checks
Local antivirus and phishing checks
Sampled scripts and pages
Resource analysis incomplete
6 resources checked · 31 script links observed on the homepage. Partial resource coverage.
ClamAV inspects the fetched homepage HTML on our server. New scans also sample up to four linked scripts and two collected internal pages, with size and time limits. Scripts are not executed. Other downloads, private server files and logged-in pages remain outside this check. A signature match needs investigation and can be a false positive. No match is not a whole-site safety guarantee.
Exact hostname lookup uses a downloaded Phishing.Database snapshot. It does not send this domain to an external lookup API or mark sibling subdomains as harmful. Not listed does not mean safe. Snapshot age is download age, not proof that every entry was recently revalidated.
Homepage HTML only · Eight local rule families · local-security-v2
Checks use the fetched page and redirect chain. Scripts are not executed, forms are not submitted, and linked files are not downloaded. This is not a malware clearance.
Page resource inventory
Counts describe the sampled HTML, not every resource loaded by the browser. External resources are common and are not automatically harmful.
No listed local patterns observed. The limited rule set cannot detect every threat or behavior.
External threat intelligence
Local checks do not query external reputation databases. An unavailable check is never a clean result.
Registration
Domain information
Infrastructure
Network & hosting
At a glance
Infrastructure summary
A compact view of the connection, DNS and security surface. These observations describe what the scanner could verify at scan time and do not prove ownership or ongoing availability.
Page telemetry
Observed page statistics
These counters describe the fetched response and sampled HTML. Script counts describe references in the markup, not a complete browser network log. Cookie counts cover observed response headers.
Encrypted transport
TLS certificate
Resolution
DNS footprint
DNSKEY presence does not verify the DNSSEC signature chain. Missing records can mean no record was returned or the lookup was unavailable.
3.165.136.117TTL —3.165.136.78TTL —3.165.136.8TTL —3.165.136.88TTL —2600:9000:2729:1200:18:2003:bfc0:93a1TTL —2600:9000:2729:200:18:2003:bfc0:93a1TTL —2600:9000:2729:3200:18:2003:bfc0:93a1TTL —2600:9000:2729:5c00:18:2003:bfc0:93a1TTL —2600:9000:2729:9e00:18:2003:bfc0:93a1TTL —2600:9000:2729:a400:18:2003:bfc0:93a1TTL —2600:9000:2729:b800:18:2003:bfc0:93a1TTL —2600:9000:2729:ee00:18:2003:bfc0:93a1TTL —ns1.dnsimple-edge.comTTL —ns2.dnsimple-edge.netTTL —ns3.dnsimple-edge.ioTTL —ns4.dnsimple-edge.orgTTL —10 mx1.forwardemail.netTTL —10 mx2.forwardemail.netTTL —forward-email-site-verification=6MYgGWeEyJTTL —v=spf1 include:forwardemail.net a mx ip4:140.211.169.12 include:mailgun.org ~allTTL —DNS observations · no external lookup API
Domain email protection
Exact-host SPF and DMARC observations help the owner investigate email impersonation risks. They are separate from website malware checks and do not change the Safety Score.
What to do next
Review the records with your mail administrator. Inventory legitimate senders and test SPF and DKIM alignment before enforcing a stricter DMARC policy. Fix duplicate records and investigate overly permissive SPF rules.
This bounded check does not send email, probe SMTP, evaluate recursive SPF includes, verify DKIM signatures or apply organizational-domain DMARC inheritance. A missing subdomain record does not prove that no inherited protection exists. A DNS timeout is unknown, not an absent record. A policy record is not proof that messages authenticate successfully.
Responsible disclosure
security.txt
No readable security.txt file was observed at the standard locations. This is informational and is not evidence of malware.
Browser protections
Security headers
Response headers
Cookie protections
No Set-Cookie header was observed on the sampled homepage response. Other pages may set cookies separately.
Detected stack
Technologies
Versions are shown only when publicly exposed by the page or response headers. An observed version is not, by itself, proof of a vulnerability.
JavaScript library advisories
4 sampled JavaScript files checked locally with Retire.js. Database snapshot: 2026-09-30T02:40:06.930Z.
A version match is not proof that the website is infected or that an issue is exploitable here. Owners should review the advisory, check whether their code is affected and test an update. Up to four external script files are sampled, not every dependency, inline script or dynamically loaded resource.
Recommended maintenance checks
About this website
What the site says about itself
SPDX is an open standard for communicating software bill of material information, including provenance, license, security, and other related information. SPDX reduces redundant work by providing common formats for organizations and communities to share important data, thereby streamlining and improving compliance, security, and dependability. The SPDX specification is recognized as the international open standard for security, license compliance, and other software supply chain artifacts as ISO/IEC 5962:2021.
This is publisher supplied information. The independent safety findings are shown separately.
Structured facts
Website identity & response
Connection path
Redirect chain
The chain is shown exactly as observed by the scanner. A redirect is not itself a malware finding, but unexpected domains or an HTTP downgrade deserve review.
Compared with the previous scan
What changed
A comparison will appear after the next completed scan.
Explainable matching
Digital fingerprint
Comparable components help find technically related websites. A match does not prove common ownership.
Material changes only
Change history
Show change history
No meaningful changes recorded yet.
Visual evidence
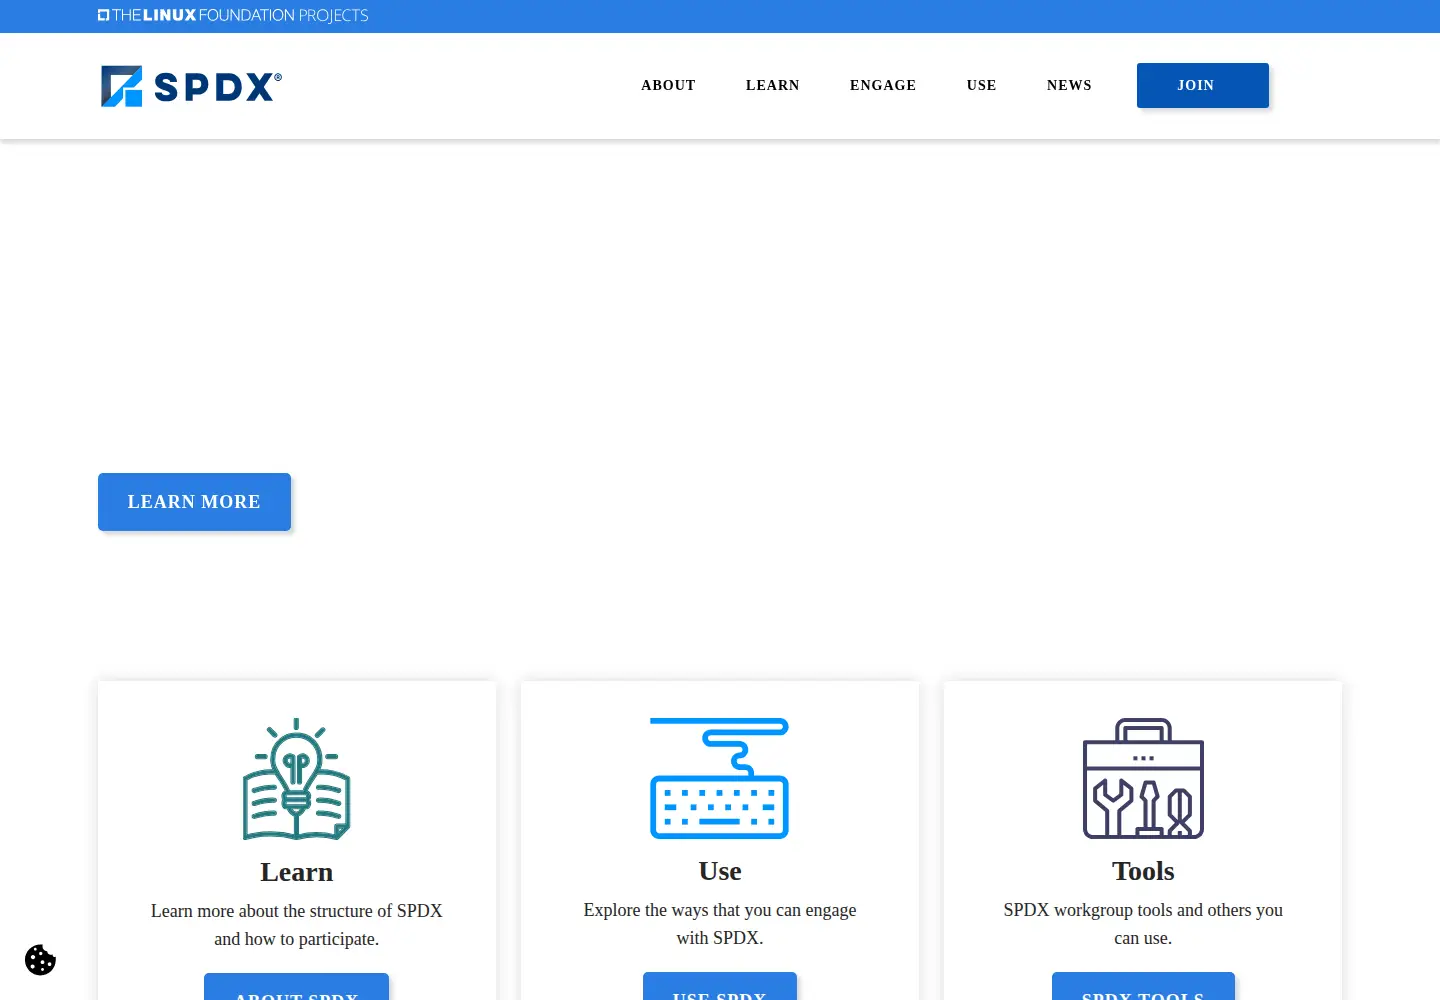
Website screenshot
For site owners
Show your verified trust report
Place this lightweight badge in your footer to show visitors an independent, dated WebsiteVirusScanner report. It can increase visitor confidence, but it never changes or guarantees the score.
Use the current report link so visitors can verify the evidence. A badge is a transparency signal, not a paid ranking boost.
Questions about spdx.org
FAQ
Is spdx.org safe to visit?
The latest Safety Score is 73/100 with 75% Evidence Confidence. This is a point-in-time assessment of observed technical signals, not a guarantee. Check the exact address and avoid entering payment details if anything looks unusual.
Did the scan detect malware on spdx.org?
ClamAV found no signature match in the sampled homepage HTML. External scripts, downloads and private server files were not checked. This is not a whole-site malware clearance.
When was spdx.org registered?
The public registry record shows Apr 16, 2010. Registration details may be privacy-protected or updated later.
Did spdx.org have a valid TLS certificate?
The scanner observed a valid TLS certificate using TLSv1.3. A valid certificate alone does not establish that the site is safe.
How does spdx.org describe itself?
The website's About page describes its purpose in the report above. This is publisher-supplied information and is separate from independent security findings.
Can a paid listing change this website's score?
No. Premium placement and owner-supplied pages are labelled separately. Technical evidence, the Safety Score and moderation decisions remain independent.
Share your experience with spdx.org
Community reviews are moderated and remain separate from the technical Safety Score.
Write review →