What is this website?
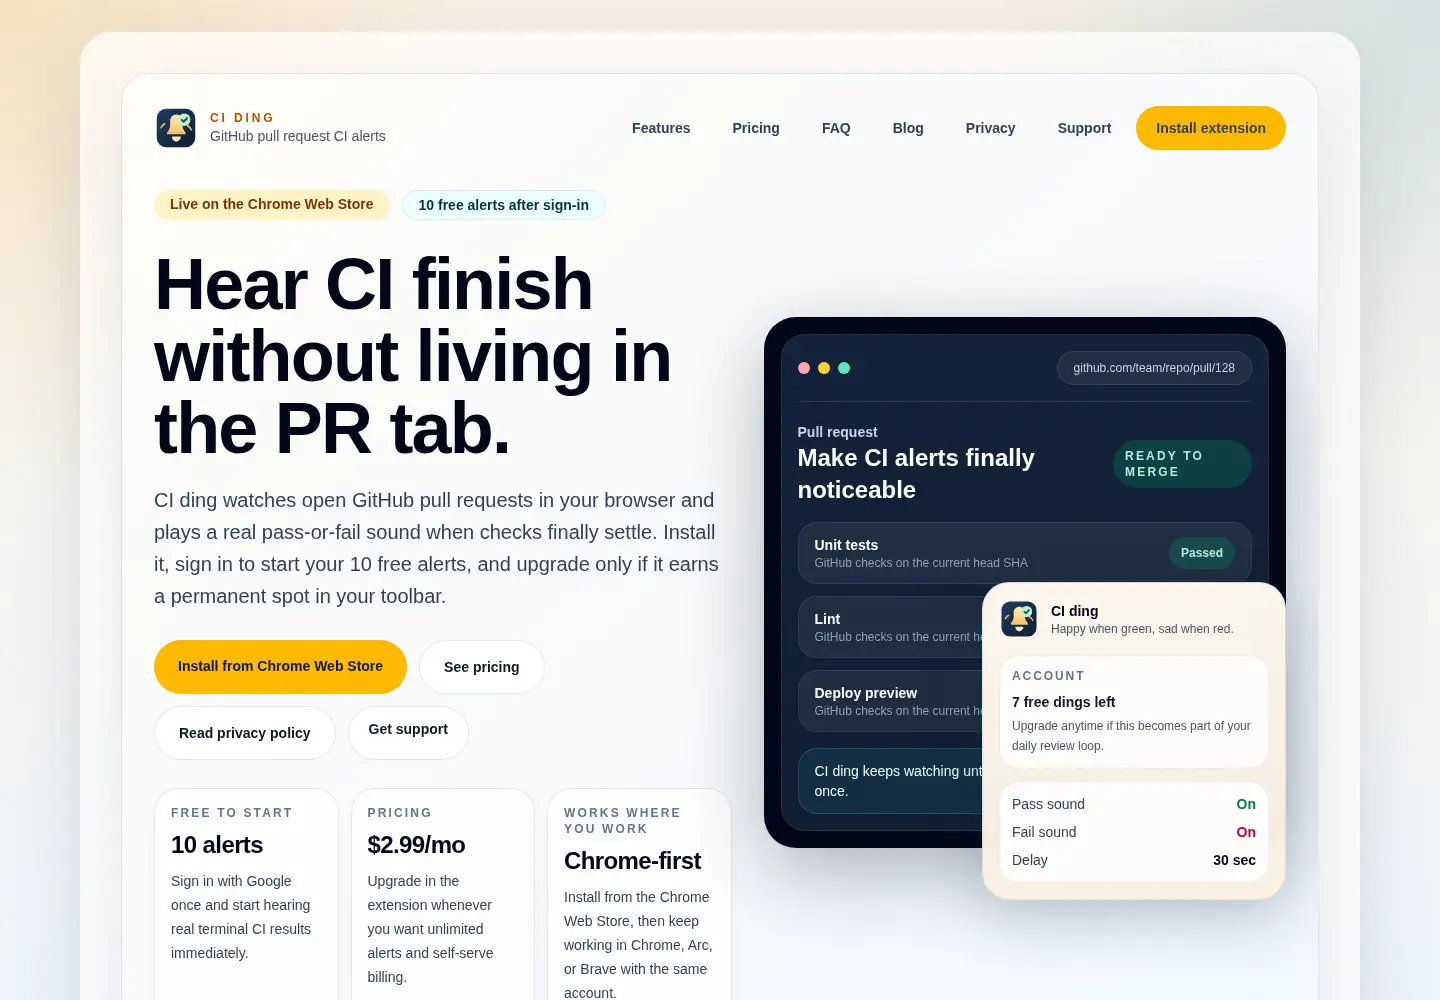
Install CI ding from the Chrome Web Store to hear GitHub pull request CI finish, get 10 free alerts after sign-in, and upgrade only when you want unlimited dings.
No listed local patterns observedHomepage-only analysis is not a malware clearance. Read the scope and findings below.
How to read this report
Safety Score evaluates observed signals. Evidence Confidence measures how complete, direct, fresh, and consistent those signals are.
No automated scan can guarantee that a website is safe.
Current report context
What changed since the last scan
- No earlier report to compare
What this scan could verify · 6 observed, 0 unavailable
Unavailable and unperformed checks are not clean results. The detailed evidence below remains the source for each conclusion.
Independent evidence brief
What we observed about ciding.app
The latest scan examined 10 public pages on ciding.app. Website descriptions below come from the site itself. Registration, connection and threat findings were checked separately.
Purpose and visible content
On its homepage, the site says: Install CI ding from the Chrome Web Store to hear GitHub pull request CI finish, get 10 free alerts after sign-in, and upgrade only…
- Support | CI dingSupport options for CI ding, including setup help, billing guidance, and account troubleshooting guidance.
- Blog | CI dingNotes from CI ding on developer focus, pull request workflows, context switching, and staying in flow while work…
- The Hidden Cost of Waiting on CI | CI…Why waiting on CI quietly fragments attention, slows pull request cycles, and makes teams feel slower than they…
Registrar and domain history
Registered on Apr 4, 2026. Registrar: Tucows Domains Inc.
Recorded expiry date: Apr 4, 2027. Registry data can change.
Connection and hosting evidence
The checked homepage returned HTTP 200 in about 1000 ms.
A valid TLS certificate was observed, expiring Dec 28, 2026.
Threat checks and score context
External malware-provider coverage was unavailable. The report does not treat this missing check as a clean result.
Safety Score: 66/100. Evidence Confidence: 75%. These measure different things.
Community reviews of ciding.app
No approved reviews yet
Visitor experiences are separate from the independent technical Safety Score.
Visitor opinions remain separate from the technical Safety Score.
Public content profile
Pages reviewed on ciding.app
We sampled public pages from this website to understand its subject and contact paths. The titles and short descriptions below come from the website itself. They are not endorsements or independent safety findings.
Public page evidence
Topics and keywords observed on ciding.app
These phrases were extracted locally from sampled public page metadata. They are observations, not search-volume or ranking estimates.
At a glance
Key findings
Report is current
The displayed evidence comes from the published immutable scan.
Confidence is separate
Unavailable evidence is shown as missing and never counted as clean.
Verify before sensitive actions
Check the exact URL and context before payments, credentials, or downloads.
Fully explainable
Why this score?
Threat providers were unavailable. The neutral uncertainty baseline is not a clean verdict.
Domain registration age and expiry were checked.
Observed DNS records and network address were checked.
Observed certificate validity and TLS protocol were checked.
Observed security header values were checked for basic protective settings. Empty values, disabled HSTS and unrecognized values receive no credit. This is not a complete browser-policy validation.
Observed site metadata and About page were checked. Publisher-supplied details are not independently verified.
Popularity is weak context, not proof of safety. Unranked sites use a neutral baseline.
Observed HTTP status and final connection scheme were checked.
Server-side analysis
Automated security checks
Local antivirus and phishing checks
Sampled scripts and pages
Resource analysis incomplete
6 resources checked · 10 script links observed on the homepage. Partial resource coverage.
ClamAV inspects the fetched homepage HTML on our server. New scans also sample up to four linked scripts and two collected internal pages, with size and time limits. Scripts are not executed. Other downloads, private server files and logged-in pages remain outside this check. A signature match needs investigation and can be a false positive. No match is not a whole-site safety guarantee.
Exact hostname lookup uses a downloaded Phishing.Database snapshot. It does not send this domain to an external lookup API or mark sibling subdomains as harmful. Not listed does not mean safe. Snapshot age is download age, not proof that every entry was recently revalidated.
Homepage HTML only · Eight local rule families · local-security-v2
Checks use the fetched page and redirect chain. Scripts are not executed, forms are not submitted, and linked files are not downloaded. This is not a malware clearance.
Page resource inventory
Counts describe the sampled HTML, not every resource loaded by the browser. External resources are common and are not automatically harmful.
No listed local patterns observed. The limited rule set cannot detect every threat or behavior.
External threat intelligence
Local checks do not query external reputation databases. An unavailable check is never a clean result.
Registration
Domain information
Infrastructure
Network & hosting
At a glance
Infrastructure summary
A compact view of the connection, DNS and security surface. These observations describe what the scanner could verify at scan time and do not prove ownership or ongoing availability.
Page telemetry
Observed page statistics
These counters describe the fetched response and sampled HTML. Script counts describe references in the markup, not a complete browser network log. Cookie counts cover observed response headers.
Encrypted transport
TLS certificate
Resolution
DNS footprint
DNSKEY presence does not verify the DNSSEC signature chain. Missing records can mean no record was returned or the lookup was unavailable.
188.114.96.3TTL —188.114.97.3TTL —2a06:98c1:3120::2TTL —2a06:98c1:3121::2TTL —guy.ns.cloudflare.comTTL —kim.ns.cloudflare.comTTL —10 mx.hover.com.cust.hostedemail.comTTL —google-site-verification=6qi6qx2wWi3NIfyRjXiphvRh97jHP2TIUL0hhcDqHSUTTL —DNS observations · no external lookup API
Domain email protection
Exact-host SPF and DMARC observations help the owner investigate email impersonation risks. They are separate from website malware checks and do not change the Safety Score.
What to do next
Review the records with your mail administrator. Inventory legitimate senders and test SPF and DKIM alignment before enforcing a stricter DMARC policy. Fix duplicate records and investigate overly permissive SPF rules.
This bounded check does not send email, probe SMTP, evaluate recursive SPF includes, verify DKIM signatures or apply organizational-domain DMARC inheritance. A missing subdomain record does not prove that no inherited protection exists. A DNS timeout is unknown, not an absent record. A policy record is not proof that messages authenticate successfully.
Responsible disclosure
security.txt
No readable security.txt file was observed at the standard locations. This is informational and is not evidence of malware.
Browser protections
Security headers
Header evidence is unavailable. Missing data is not treated as a clean result or proof of compromise.
Response headers
Cookie protections
No Set-Cookie header was observed on the sampled homepage response. Other pages may set cookies separately.
Detected stack
Technologies
Versions are shown only when publicly exposed by the page or response headers. An observed version is not, by itself, proof of a vulnerability.
JavaScript library advisories
4 sampled JavaScript files checked locally with Retire.js. Database snapshot: 2026-10-09T02:40:13.041Z.
A version match is not proof that the website is infected or that an issue is exploitable here. Owners should review the advisory, check whether their code is affected and test an update. Up to four external script files are sampled, not every dependency, inline script or dynamically loaded resource.
Recommended maintenance checks
Structured facts
Website identity & response
Connection path
Redirect chain
No redirect hop was recorded for the sampled homepage.
Compared with the previous scan
What changed
A comparison will appear after the next completed scan.
Explainable matching
Digital fingerprint
Comparable components help find technically related websites. A match does not prove common ownership.
Material changes only
Change history
Show change history
No meaningful changes recorded yet.
Visual evidence
Website screenshot
For site owners
Show your verified trust report
Place this lightweight badge in your footer to show visitors an independent, dated WebsiteVirusScanner report. It can increase visitor confidence, but it never changes or guarantees the score.
Use the current report link so visitors can verify the evidence. A badge is a transparency signal, not a paid ranking boost.
Questions about ciding.app
FAQ
Is ciding.app safe to visit?
The latest Safety Score is 66/100 with 75% Evidence Confidence. This is a point-in-time assessment of observed technical signals, not a guarantee. Check the exact address and avoid entering payment details if anything looks unusual.
Did the scan detect malware on ciding.app?
ClamAV found no signature match in the sampled homepage HTML. External scripts, downloads and private server files were not checked. This is not a whole-site malware clearance.
When was ciding.app registered?
The public registry record shows Apr 4, 2026. Registration details may be privacy-protected or updated later.
Did ciding.app have a valid TLS certificate?
The scanner observed a valid TLS certificate using TLSv1.3. A valid certificate alone does not establish that the site is safe.
Can a paid listing change this website's score?
No. Premium placement and owner-supplied pages are labelled separately. Technical evidence, the Safety Score and moderation decisions remain independent.
Share your experience with ciding.app
Community reviews are moderated and remain separate from the technical Safety Score.
Write review →